Audit readiness, cyber and third-party risk, GRC automation, customer trust and AI governance, from practitioners who've built these programs at global companies.
book a strategy session


Security reviews are holding up deals.
We answer questionnaires fast, then build the answer library and trust center that stop the repeats.

New vendors sit in intake for weeks.
We clear the queue and set up a process that keeps it clear.

Leadership is asking where you stand.
We keep the risk register current and turn it into reporting they can act on.

An audit is coming and the evidence is everywhere.
We get controls tested and evidence ready before the auditor asks.

You just onboarded a new GRC tool, but your GRC team doesn't have a technical resource.
We partner with you to ensure that GRC tool implementations go smoothly.
Every engagement is led by one of our principals who have combined experience of 20 years in the risk and security space in the most complex and highly regulated enterprise environments.
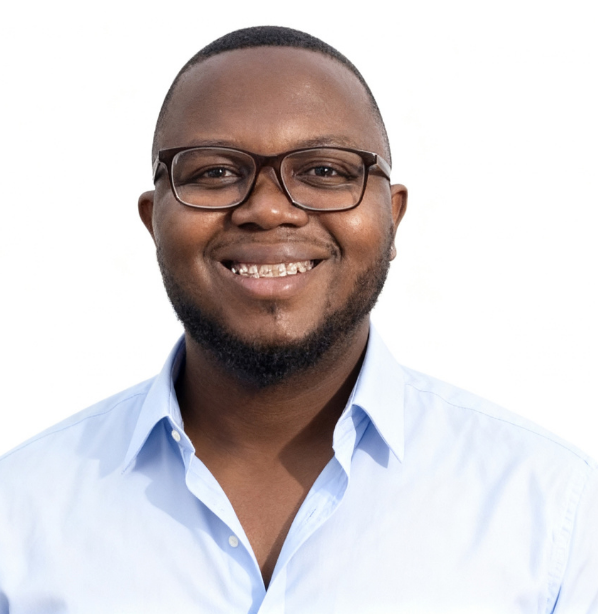
Tatenda Shoriwa spent more than eight years in security architecture across media, hospitality, enterprise software and energy. He led enterprise architecture reviews, secured large-scale cloud migrations and designed controls for generative AI after starting his career in cyber defense and threat hunting. He earned a master's in cybersecurity, Security+, GIAC GPCS and his CRISC certification.
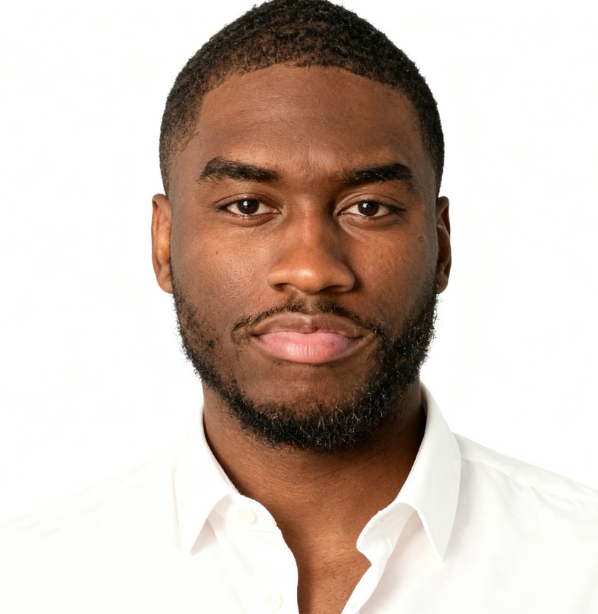
Richard built his career in governance, risk and compliance across health tech, financial services and enterprise software. He designed and implemented customer trust and security assurance programs, established AI risk governance, and ran third-party risk oversight. He earned a BS in computer science, GIAC GLED, and his CRISC certification.
A 30-minute call to understand your needs and what "done" looks like.
You get a named consultant's resume within 2 business days and interview them before anything is signed.
Work begins inside your tools (your trust platform, ticketing system and Slack) within 7 business days of a signed SOW.
A short weekly update: what closed, what's open, what's blocked.
Most security teams don't need another tool or another full-time hire.
They need experienced people who can step into the backlog and leave the program stronger.
With RASOR Center, you interview your lead before anything is signed.
We connect trust, vendor risk, cyber risk and audit work, and everything we build stays with you.
You interview the consultant who leads your work, and you approve anyone else who touches it.
Questionnaire answers, vendor reviews, the risk register and audit evidence all draw on the same controls. We work across all four, so nothing gets done twice.

Answer libraries, runbooks and documentation are yours when the engagement ends.


